BitcoinWorld
Gnosis Safe Wallet Loses $7.7 Million, and Hackers Never Had to Crack It
Key Takeaways
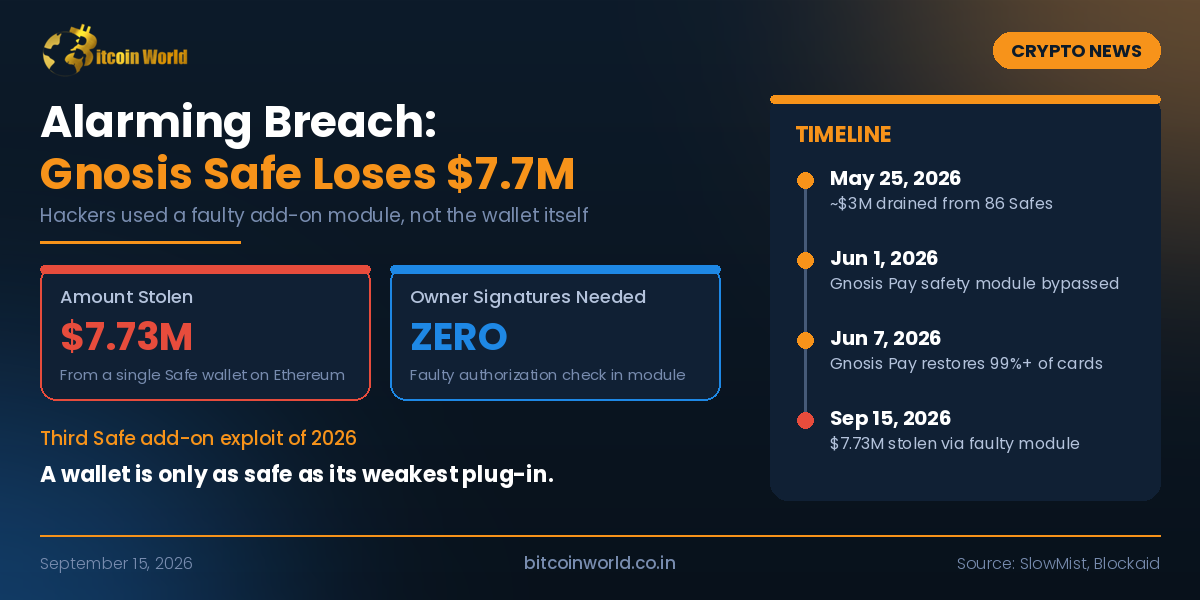
Hackers stole about $7.73 million from one Gnosis Safe wallet on September 15, 2026.
They didn’t break the wallet itself. They got in through an add-on tool connected to it.
The stolen money was passed through a trading pool the hackers set up, which made it harder to trace.
This is the third time this year that Safe wallet add-ons have been used to steal funds.
First, what is a Gnosis Safe?
Think of a Gnosis Safe as a bank locker that needs several keys to open. Companies, crypto funds and wealthy investors use it because no single person can move the money alone. That is why it has a reputation as one of the safest places to keep crypto.
Safe also lets owners plug in extra tools, called modules, that handle routine work automatically, such as moving funds to earn interest. The catch is that these tools can move money without asking for all those keys.
What went wrong
The wallet belonged to a big investor who had connected one of these automatic tools. That tool had a faulty security check. It was supposed to confirm who was giving the orders, and it didn’t do that properly.
The hackers noticed the flaw and used the tool to move the money into a trading pool they had created themselves. From there, they swapped it for other coins and walked away. The wallet owners never approved anything.
In simple terms, the locker was strong, but a side door had been left unlocked.
How it unfolded this year
May 25: About $3 million was taken from 86 Safe wallets in roughly two hours through a faulty add-on.
June 1: Hackers found a way past a safety feature in Gnosis Pay, the crypto debit card service built on Safe.
June 7: Gnosis Pay had normal card services working again for more than 99% of its users.
September 15: The $7.73 million theft happened, starting with one large transfer and followed by smaller ones over the next hour.
Why this should worry people
All three attacks follow the same pattern. The main wallet held up, but the extra tools attached to it failed. Security firms spotted this latest theft quickly, yet they still couldn’t stop it, because these transfers happen in seconds.
The fake trading pool was also a smart move by the hackers. It let them swap stolen coins on their own terms without depending on anyone else.
What happens next
We will likely see stricter checks before these add-ons can be connected to wallets. Limits on how much an add-on can move, and waiting periods before large transfers, may become standard. Wallet apps may also start warning users when a connected tool looks risky.
Conclusion
This theft doesn’t mean Gnosis Safe is broken. It does show that a wallet is only as safe as the weakest tool plugged into it. If you use a Safe, check which add-ons are connected today, and remove any you don’t recognise or no longer use.
This post Gnosis Safe Wallet Loses $7.7 Million, and Hackers Never Had to Crack It first appeared on BitcoinWorld.
